CA/CR® CISO Console

Six questions every CISO is asked. One console that answers them.

What is Security, if not ...
continuously assessing, finding gaps and remediating them ?

With facts, not opinions: what is really configured, tested and fixed, and what is still open. Every gap becomes a remediation sprint.

ISO 27001 · NIST CSF 2.0 · CIS · PCI-DSS NIS2 · DORA · GDPR · AI Act 20+ technical security sets
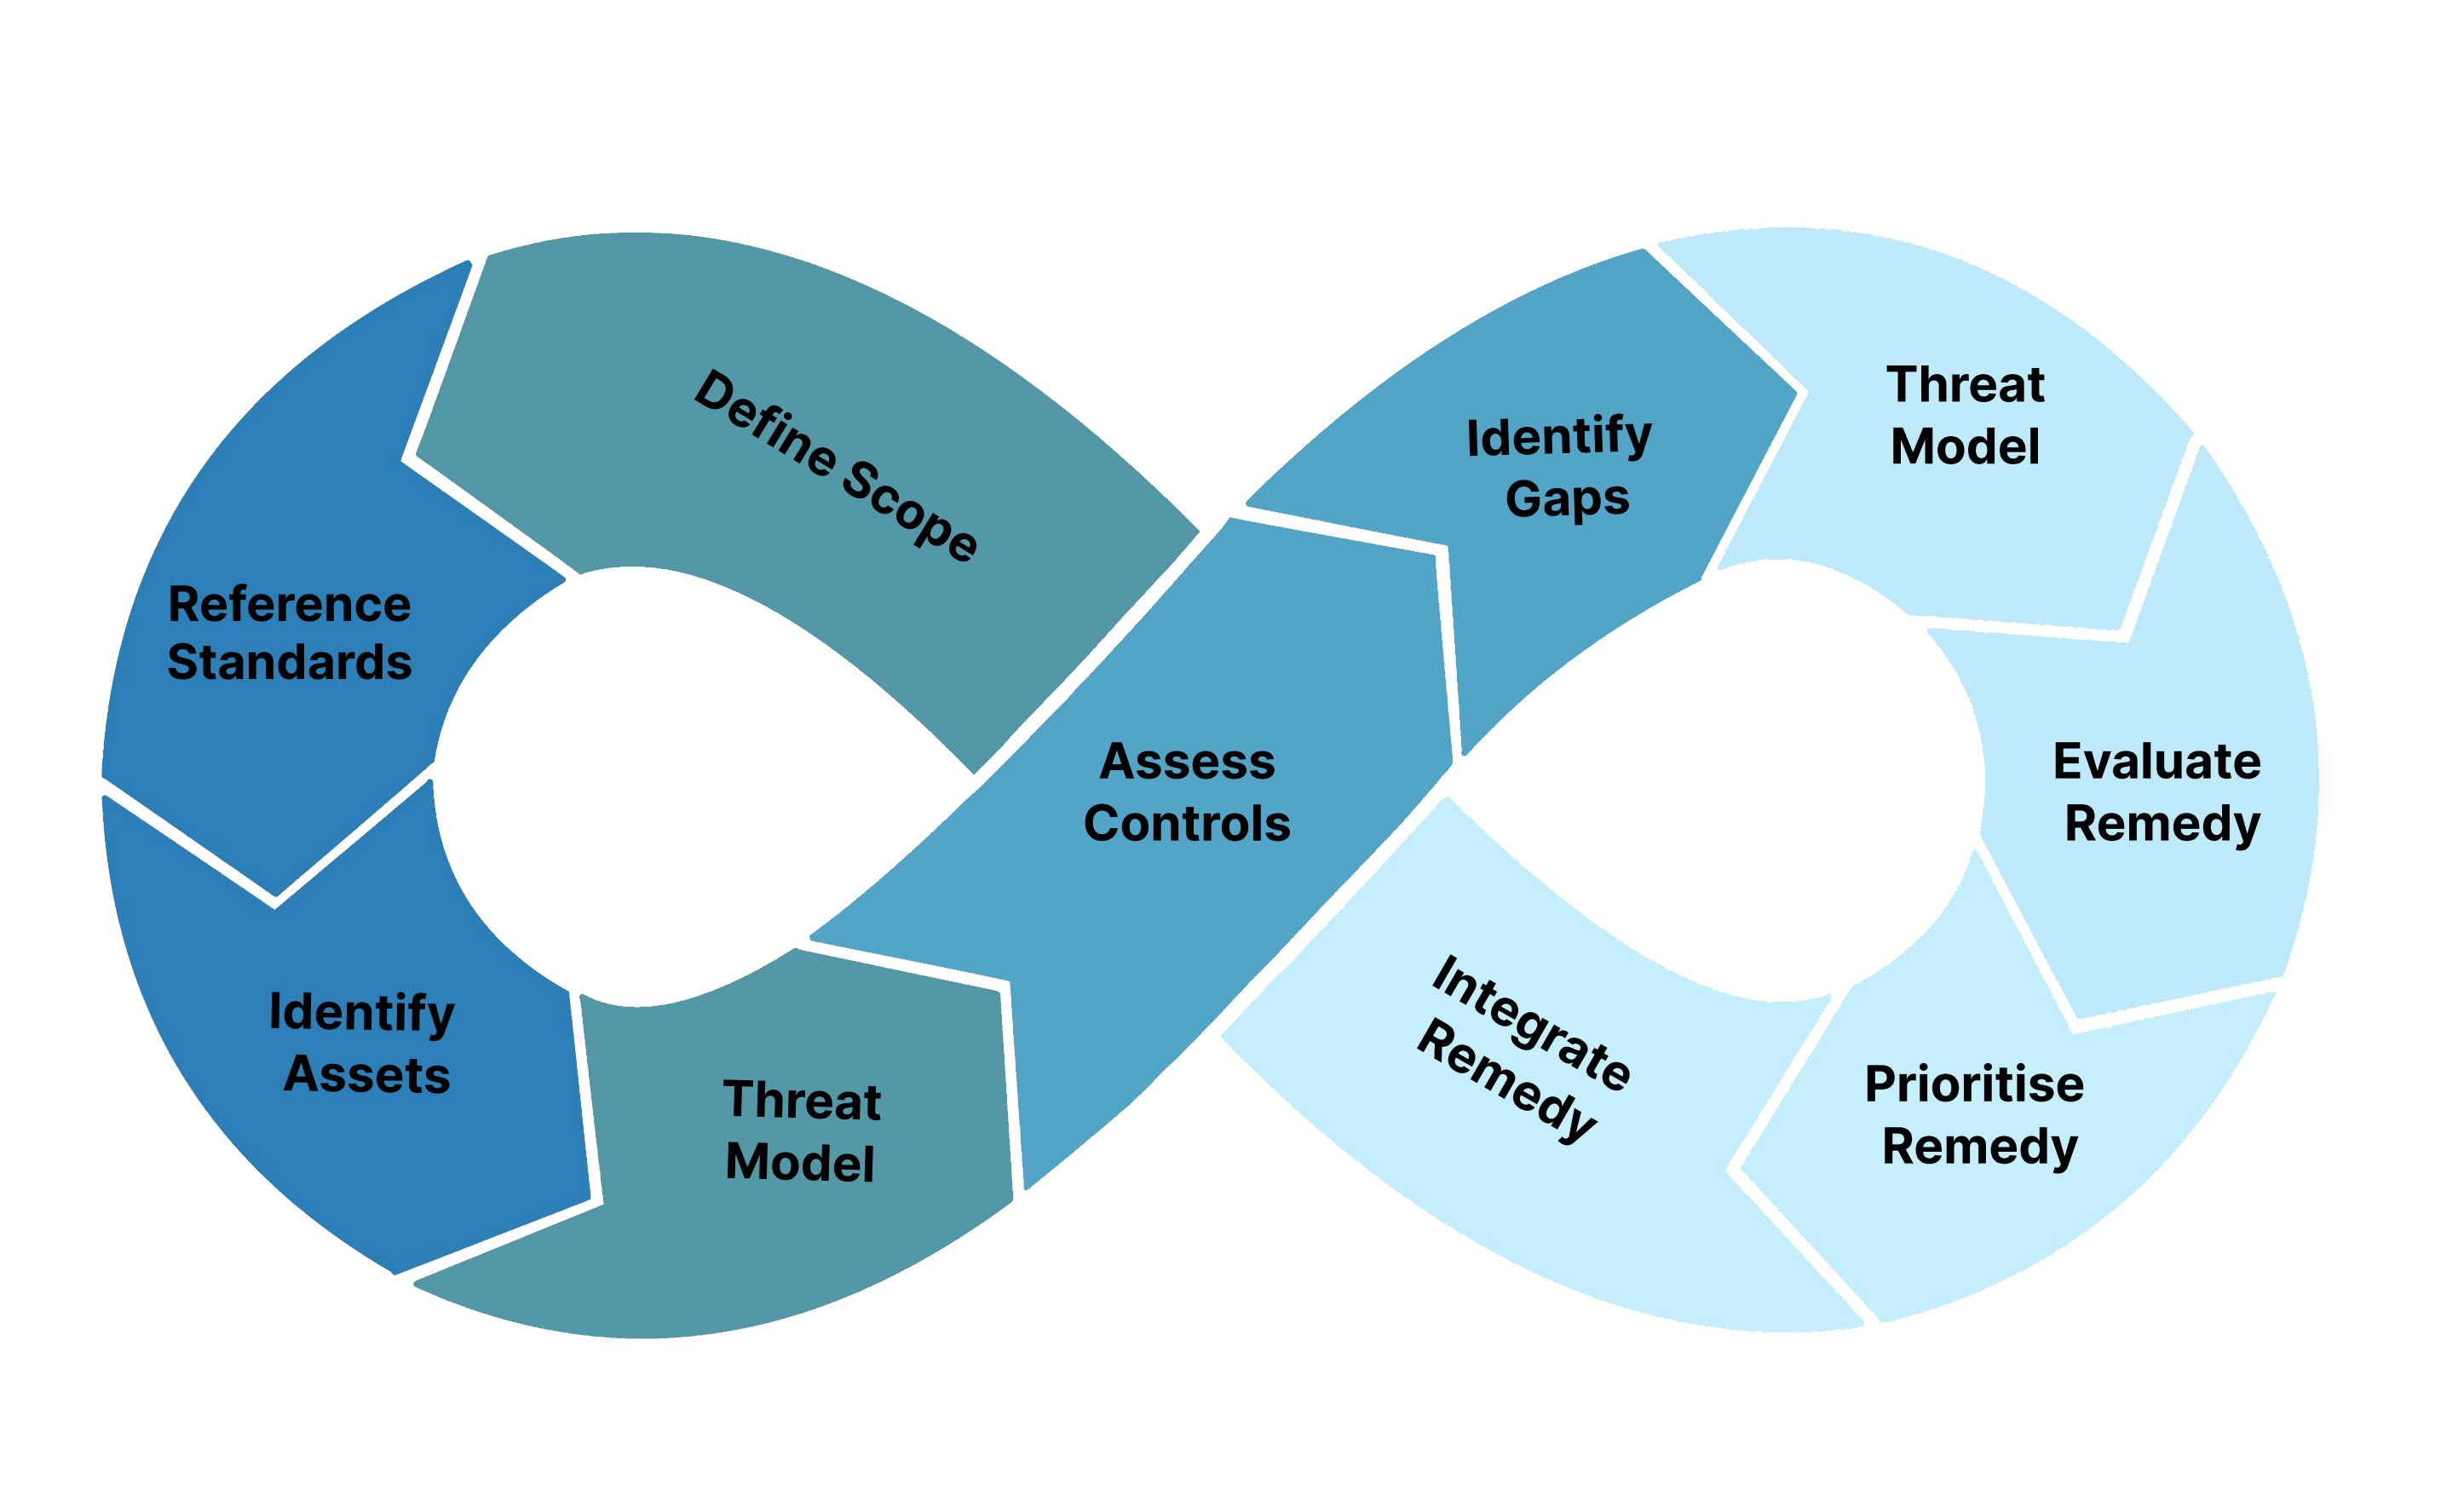
The CA/CR® cycle
The heart of the platform

CA/CR®: Continuous Assessment, Continuous Remediation.

Our proprietary, copyrighted methodology, distilled from decades of CISO work in complex enterprises. One cycle that never closes, as wide or as narrow as your resources and risk appetite allow.

AssessPick one scopea first campaign live in minutes
AssessAsk the people who knowowners answer by secure link
RemediateFix what matters firsta sprint with owners and deadlines
RemediateVerify, then go againretest, then widen the scope
Question 1

Do we meet what applies to us?

Standards, regulations and your own policies, measured from the same answers.

Standards & regulationsISO 27001, NIST CSF 2.0, CIS, PCI-DSS, NIS2, DORA, GDPR and the AI Act. Mapped once: one answer counts everywhere it applies.
Compliance postureA score per standard and per regulation, with coverage and trend, per entity and for the group.
PoliciesMore than 40 templates across 19 domains. Tailor, version, approve and export, then launch a campaign on what the policy requires.
Risk registerLikelihood × impact, owners and treatment. See where each risk started, stands today and is heading, and turn it into a campaign.
Question 2

Are we actually secure?

Compliant is not the same as secure, so the two are scored separately and never blended.

Compliance posture

ISO 2700186%
NIS279%
Example figures

Security posture

Active Directory58%
VMware49%
Example figures
Technical security setsMore than twenty sets of concrete hardening measures: Active Directory, Microsoft 365, Windows 11, VMware vSphere, networks, servers, web applications, OT and more. New sets are added continuously.
ProceduresOne for every technical set. The policy says what and why; the procedure says how, and assessing the set shows whether it is followed.
Security postureA separate score per technology. A high compliance score cannot hide a weak configuration.
Daily posture feedsMicrosoft 365 and MFA settings are read every day, so the score follows the real configuration.
Penetration test follow-upFindings from any test, classified by CWE and OWASP, tracked through fix and retest.
Question 3

What do we depend on?

Know which systems carry which processes, and how fast each must be back, before one of them fails.

Scope registerYour critical systems with owner, criticality, vendor, data and location, plus recovery objectives (RTO and RPO), recovery procedures and emergency contacts.
Process registerEach business process with its impact and the scopes that sustain it. A gap is flagged when a recovery target is tighter than the systems underneath can deliver.
Business continuity planGenerated as a report from your processes and scopes, reviewed, approved and versioned.
Scope postureThe security state of each critical system, trended over time.
EntitiesSubsidiaries, branches and units, each with its own scopes and owners, rolled into one group view.
Question 4

Can we trust our suppliers?

What the supplier says, beside what the internet shows.

Third-party registerEvery supplier with criticality, risk level, owner and the entities it serves.
Supplier questionnairesScoped to what each supplier does for you, answered through a secure link, with evidence.
ReconX integrationAn objective external security grade for each supplier, shown side by side with the supplier's own answers.
Satisfaction evaluationA yearly rating on security, quality, price and execution, with a recommended action for each supplier.
Supplier security annexesContract annexes that match the questionnaire the supplier is assessed against.
Question 5

What went wrong, and who is fixing it?

Whatever exposes a weakness starts a sprint with a named owner and a deadline.

Incident registerFrom detection to lessons learned. Impact scored on confidentiality, integrity and availability; GDPR, NIS2, DORA and AI Act reporting flagged on time.
CA/CR® CampaignsRemediation sprints across scopes and entities, launched from a risk, a policy, an incident or a finding, followed live.
Contributors by secure linkExperts and suppliers take part without an account. Unlimited, no seats to count.
My Actions and team boardEveryone sees what to do next; managers see who is behind and who has gone silent.
Question 6

Can we prove it?

When the board, an auditor, a regulator or an insurer asks, the answer is already written and it matches the facts.

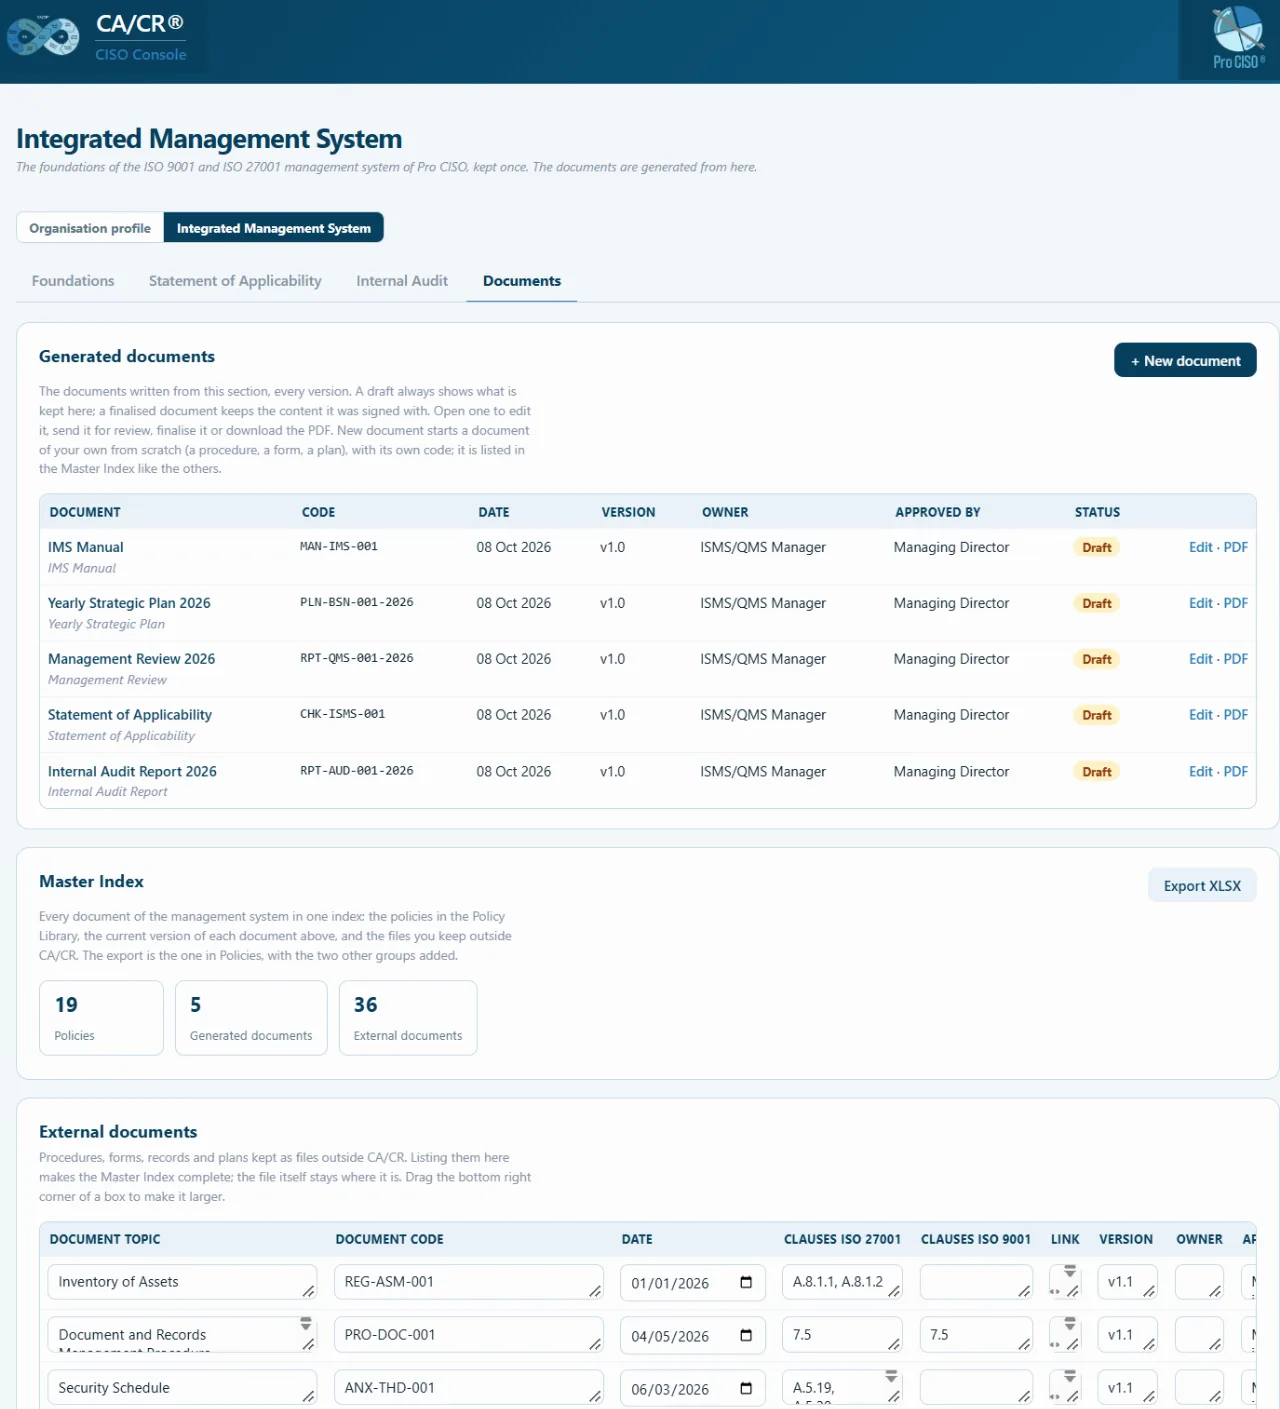
CA/CR® CISO Console - Integrated Management System: generated documents, Master Index and external documents
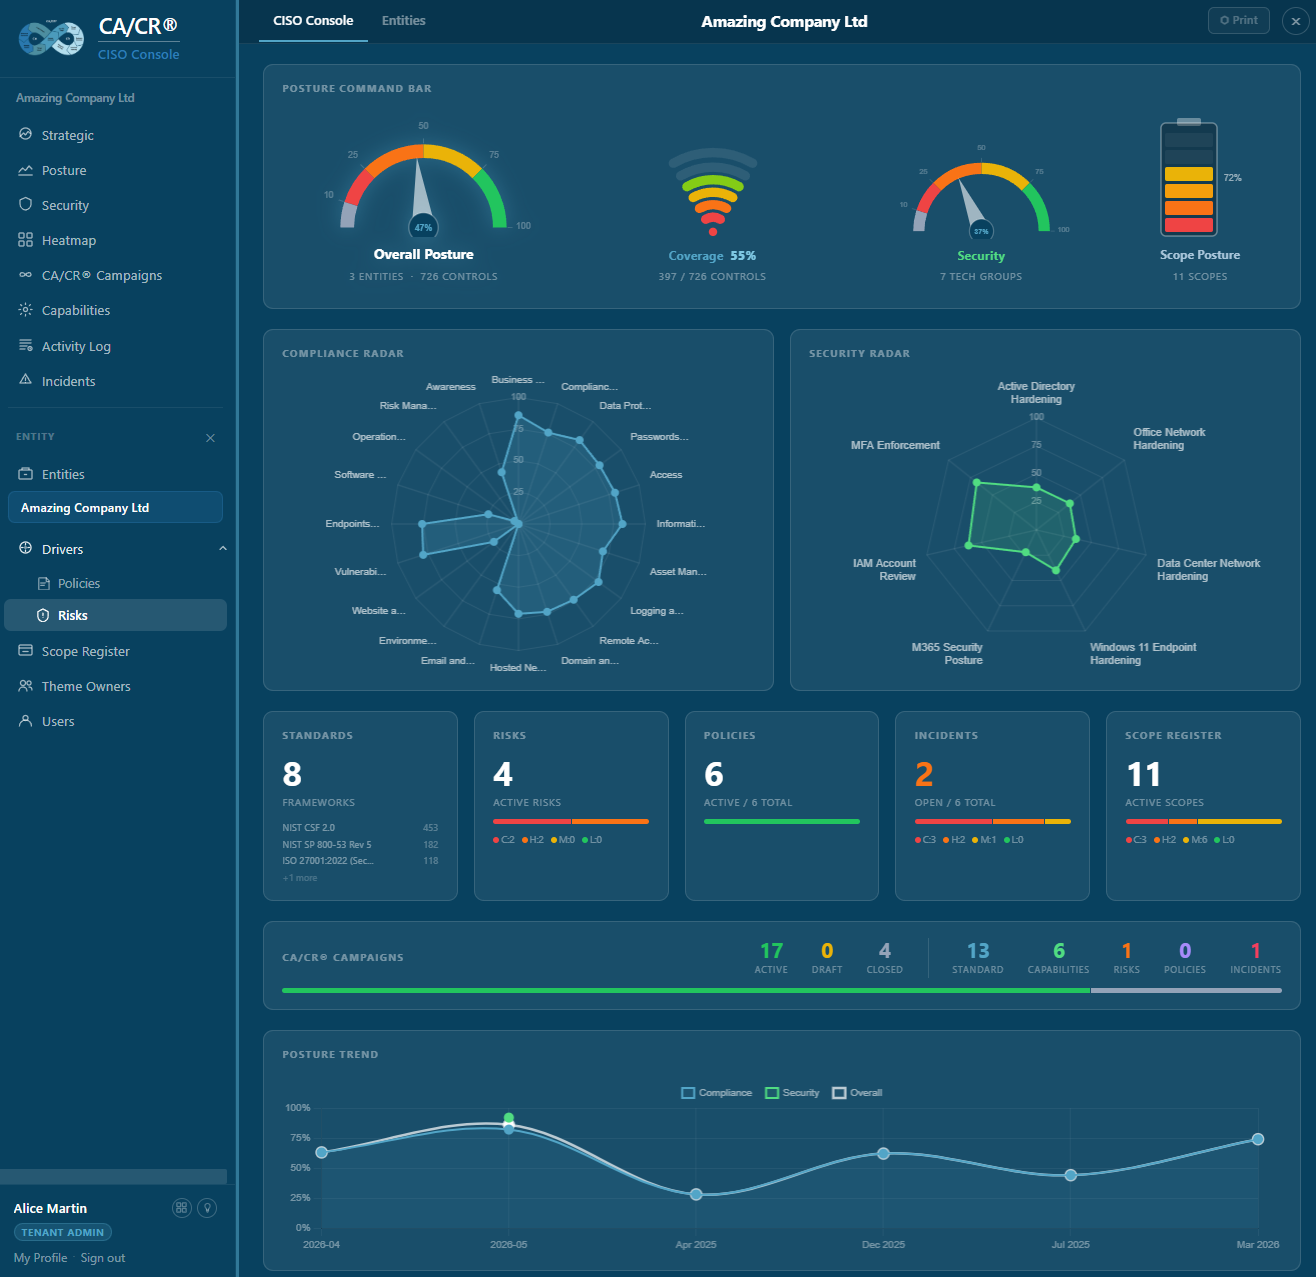
CISO dashboardsStrategic overview, heatmaps, dials and trends, from the group down to one control.
Report engineCISO, standards, regulations, security, risk, supplier, campaign and continuity reports. Reviewed, approved and locked as a record.
Integrated Management SystemNewScope, context, objectives, Statement of Applicability, audits and findings kept once. IMS Manual, Strategic Plan, Management Review and Audit Report generated for ISO 27001 and ISO 9001 as one system.
Master IndexEvery policy, generated document, procedure and external reference with code, version, dates and owner.
Who it is for

One method. Sized to the way you work.

See every entity. Compare them. Raise the floor.

One view, every entityeach subsidiary keeps its own scope, owners and posture; you see them side by side and consolidated
One campaign, all entitiesthe same measure across the group
One standard of hardeningso "secure" means the same thing in every country
Board and regulator reportsper entity and for the group
Pricing

Start where you are. Grow at your pace.

Standard
€5,000 / year

The full CA/CR® cycle on your standards and regulations.

  • Standards and regulations, compliance posture
  • CA/CR® Campaigns, scope register, incident register
  • Dashboards and version-controlled reports
  • 5 entities, unlimited users and contributors
Get started
Enterprise
Contact sales

Everything in Professional, shaped to you.

  • Integrated Management System (ISO 27001 + ISO 9001)
  • Additional third parties
  • Automated ReconX supplier scans
  • Sector and industry sets on demand, e.g. maritime (IACS UR E26 / E27)
  • API integrations
Contact sales
About Pro CISO®

Built by Pro CISO®, your dedicated security partner.

Founded in Amsterdam in 2020, Pro CISO® is a cybersecurity company certified ISO 9001:2015 and ISO 27001:2022. We simplify cybersecurity management through our Pro CISO-as-a-Service offering that provides a front-facing CISO, a pool of specialists certified in multiple domains, and a toolkit of solutions that help organisations achieve and maintain cybersecurity resilience. CA/CR® CISO Console is the platform born from that practice.

2020founded in Amsterdam
CA/CR®proprietary method

Start with one scope. See the difference in one sprint.

A first campaign is live in minutes. We will walk you through it.

Plan your first sprint